28JulThreat Modeling for Systems with AI Componentsby Amir Marzani, B.Eng., Consultant Security EngineeringLearn how to systematically identify threats in AI-based applications.
30JunDDoS Red Teaming: Realistic Attack Scenario or Unnecessary Escalation?by Fabian MittermairRed teaming is meant to be realistic. But when does realism become too much?
24AprThe Return of Identity Theft: In the Age of Phishing and BECby Thomas LangthalerEveryone talks about ransomware. Understandably so: encrypted data, ransom demands, PR disasters—it naturally attracts attention. But while we're focused on the skull-and-crossbones in the headline, an old discipline is quietly making its return to the cyber threat landscape: identity theft.
17AprNot All That Glitters Is Gold: Pre-Employment Screeningby Christoph ZajicThe Austrian Network and Information Systems Security Act (NISG) already requires operators to ensure that employees are trustworthy, aware of their responsibilities, and qualified for their assigned roles.
17MarRansomware Attacks as Data Protection Incidents: GDPR Requirements and Reporting Obligationsby Dzevad MujezinovicRansomware attacks reached a new record high in 2024, threatening organizations worldwide. Critical sectors such as healthcare and public authorities remain prime targets, but small and medium-sized enterprises (SMEs) are increasingly affected as well. Cybercriminals are increasingly stealing data to extort ransom payments.
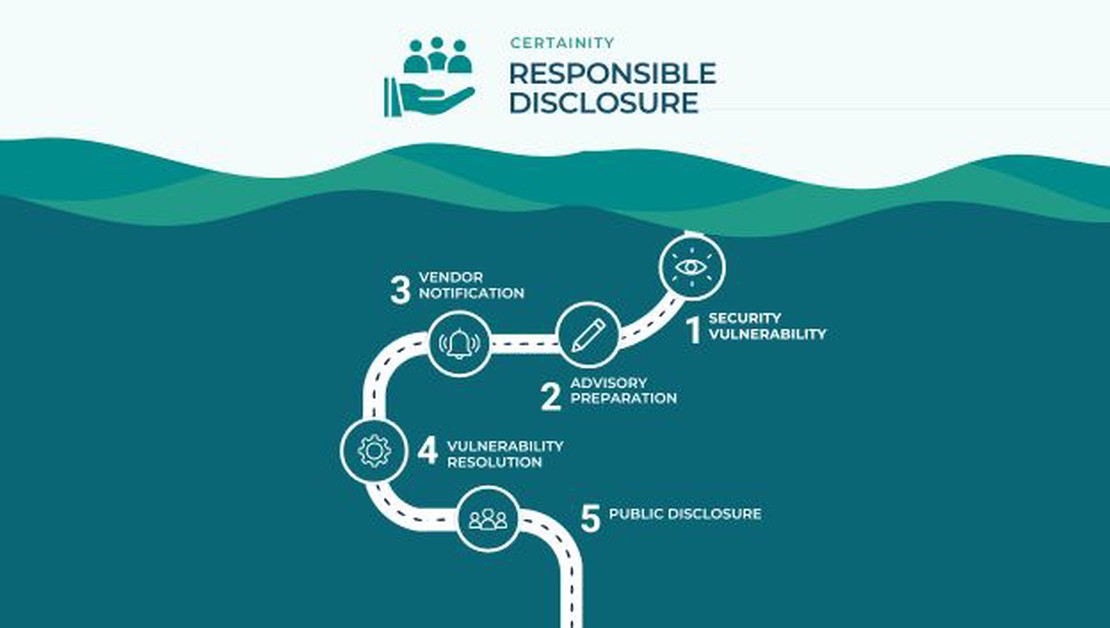
19FebResponsible Disclosure: Handling Security Vulnerabilities Responsiblyby Yuri Gbur, Sandro Einfeldt, Fabian MittermairSoftware vulnerabilities are inevitable—but how they are handled makes all the difference. Responsible Disclosure helps ensure that security flaws are remediated before they can be exploited by attackers.